The Satellite-Field Cipher
A single number of a few dozen digits defines a vast, uniquely reproducible family of Goldbach representations, arranged geometrically as a satellite field around their common midpoint. This page turns that landscape into a keystream, gives the reference code, and shows the analysis — including a candid account of what it is not. It is best understood not as a rival to standard encryption but as an instrument that happens to be unpredictable.
The object
Fix a positive integer midpoint M and consider the non-central
Goldbach representations of the even number 2M:
prime pairs (p, q) satisfying
p + q = 2M with p < q.
Every such pair is symmetric about M. Its
radius, or half-difference, is
d = M − p = q − M
       = (q − p)/2
, so the pair can equally be written
(M − d, M + d).
The satellite field of M is this same set of Goldbach
representations viewed geometrically and ordered by increasing radius
d. Thus each satellite is a Goldbach prime pair, and each radius
identifies exactly one representation of 2M. The field is
deterministic given M and finite, because
0 < d < M. Near
d = M the field reaches what we informally call its
outer skin.
Crucially the field is randomly accessible. A representation near
any chosen radius can be sought directly by testing whether
M − d and M + d are prime; there
is no need to enumerate all smaller radii first. You can therefore begin near
radius 1012 or 1040 without walking there from zero. The key
is a location in the landscape — the midpoint and starting radius
(M, x) — not merely a single number.
From field to keystream
Write the ordered radii in a chosen window as
d1 < d2 < ….
The consecutive radial gaps are
Δi = di+1 − di.
These are gaps between successive Goldbach representations when ordered by their
half-difference from the midpoint. The keystream compares such gaps in disjoint pairs:
bit i = 1 if gapa > gapb, else 0 — ties (equal gaps) are dropped.
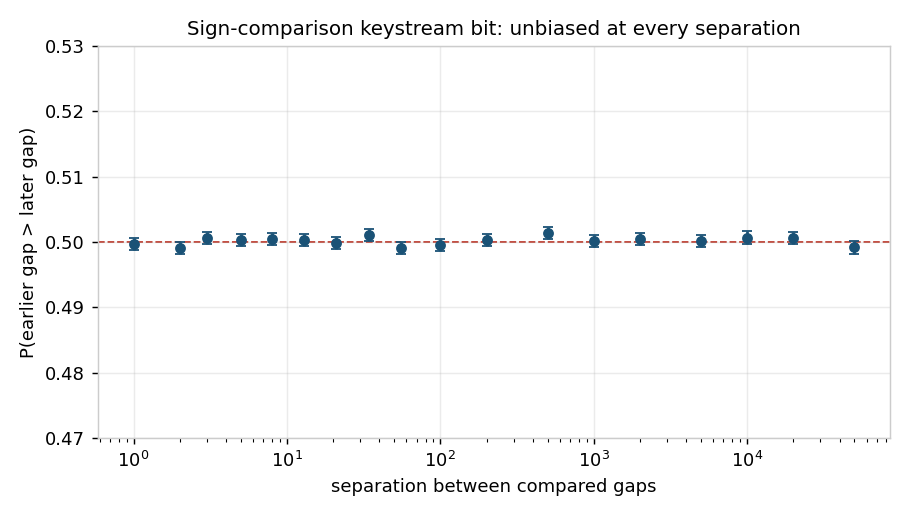
The comparison can be between the two halves of a window (a palindrome), between adjacent gaps, or across two windows started at different radii. All rest on the same idea: within a region where the prime density is effectively constant, two gaps are taken to be exchangeable — equally likely to fall either way. Under that assumption the comparison is unbiased by symmetry, with no whitening step required. Exchangeability is not guaranteed a priori: radial density variation, dependence between nearby gaps, and the window construction could all in principle disturb it. It is therefore a claim to be tested, not a theorem — and the measurements below found no departure from it over the range examined.
The bit is a comparison, never a radial-gap magnitude. This matters: emitting the actual gaps between successive Goldbach representations would expose modular information about the underlying prime pairs and allow the midpoint to be reconstructed almost instantly. A sign comparison exposes no such direct residue information.
Reference implementation
pfxor2.py is a constant-memory, parallel generator. The key is
(M, x); the window is sized from the payload and reproduced on
decryption, so nothing but the key need be shared. The keystream is XORed with the
file, so the same command encrypts and decrypts.
# encrypt
py pfxor2.py plaintext.jpg cipher.bin -m "10**30+61" -x "10**12" --meta run.json

# decrypt (identical command, files swapped)
py pfxor2.py cipher.bin recovered.jpg -m "10**30+61" -x "10**12"
−m and −x accept plain decimals or Python expressions. The tool prints the radius range it consumed and warns if the combined keyspace falls below 100 bits or if the window strays into the field’s outer skin.
Keyspace and scale
The key (M, x) draws entropy from both parts, and the search over
them is joint — a wrong midpoint makes every radius wrong. A 20-digit
midpoint yields approximately 122 bits of combined search space (66 from M,
56 from the radius after discounting hit-spacing) — approaching the scale of
AES-128 but not matching it. A larger midpoint raises both figures; see the note
on quantum resistance below. The same
midpoint holds roughly 3.5 petabytes of keystream before the field is
exhausted, so a single M is effectively inexhaustible.
Field capacity scales as M / ln²M and keyspace as roughly 2 log⊂2 M — both driven by the same parameter. There is no awkward regime where one is adequate and the other is not. Twenty digits is a natural operating point: strong key, vast field, and small enough that primality tests fit in machine words.
Analysis
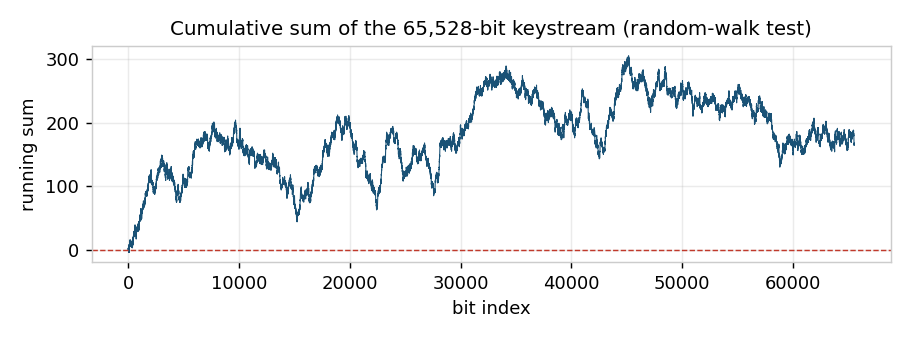
An all-zeros file was encrypted with a randomly chosen 20-digit midpoint, so the ciphertext is the raw keystream. It was then regenerated independently on separate hardware from the key alone — byte-for-byte identical — and subjected to a statistical battery over its 65,528 bits.
| Test | Result | p-value |
|---|---|---|
| Monobit frequency | pass | 0.52 |
| Block frequency (128-bit) | pass | 0.56 |
| Runs | pass | 0.03 |
| Longest run of ones | pass | 0.83 |
| Cumulative sums | pass | 0.47 |
| Approximate entropy (m=8) | pass | 0.70 |
| Byte distribution (χ²) | pass | 0.72 |
| Autocorrelation (lags 1–32) | pass | 0.54 |
Byte entropy was 7.979 of 8 bits — exactly the value a random sample of this size should give — and both zlib and lzma expanded the file, as incompressible data does.
What this does and does not establish
Passing a statistical battery demonstrates the absence of crude bias. It is the weakest thing that could be true, and it is not evidence of security. A known attack against a related construction — one that reconstructs the midpoint from emitted gap magnitudes — would also pass every test above, because it exploits structure rather than bias. This cipher withholds magnitudes precisely to close that route, but the deeper question — whether the sequence of sign comparisons can be inverted to recover the midpoint — is open. No one has answered it, and until someone tries hard and fails, this is a research object, not a deployable cipher.
Possible roles, if the construction survives analysis
Honestly appraised, this is far slower than AES and occupies the same functional slot as a stream cipher. Its merit is not throughput. The following are research directions rather than present recommendations — each is a high-value setting in which an unanalysed cipher should not yet be trusted, listed to show where the object might one day fit rather than where it belongs today:
- Key masking. Mask a 32-byte key in under a second; let AES carry the bulk. The slow primitive touches only the small, high-value secret. Note that XOR alone is malleable and provides no integrity: true key wrapping would require an added authentication step, which this construction does not yet provide.
- Cascade layering. AES first, then this, on data that must outlive the assumptions behind a single cipher — seed phrases, recovery material, cold archives. Two unrelated foundations: a designed S-box, and the distribution of the primes.
- Post-quantum posture. No Shor-type attack is presently apparent, because the construction exposes no known algebraic structure of the kind Shor’s algorithm exploits; other specialised quantum attacks have not been investigated. Generic Grover search would roughly halve the effective search space, so the 122-bit, 20-digit operating point offers only about 61 bits against idealised quantum brute force. Targeting ~128-bit quantum resistance would need a larger midpoint — on the order of 40 digits, subject to the exact keyspace calculation. This posture is table stakes for symmetric schemes rather than a distinction, but it is worth stating precisely.
-
Reproducible delayed reveal. A generated sequence or ciphertext
can be published first and its midpoint and radius disclosed later, letting
others reproduce it independently. This much is sound. Genuine commitment,
authorship or provenance claims would require additional authentication —
a timestamp or signature — together with an analysis establishing that no
alternative
(M, x)can produce the same output.
The most durable outcome is not the cipher but the question it poses: how much of a midpoint’s identity is recoverable from its satellite field — equivalently, from the ordered Goldbach representations of 2M when only comparisons between their radial gaps are revealed? That is a genuinely novel question about the primes, and it is a better one than whether this makes a good stream cipher.
The construction and analysis on this page were developed in a working collaboration between the author and AI systems — the “AI and I” method described elsewhere on this site. The reference code is provided as-is, for study and attack rather than for protecting anything that matters.